Detection & response
SOC Homelab
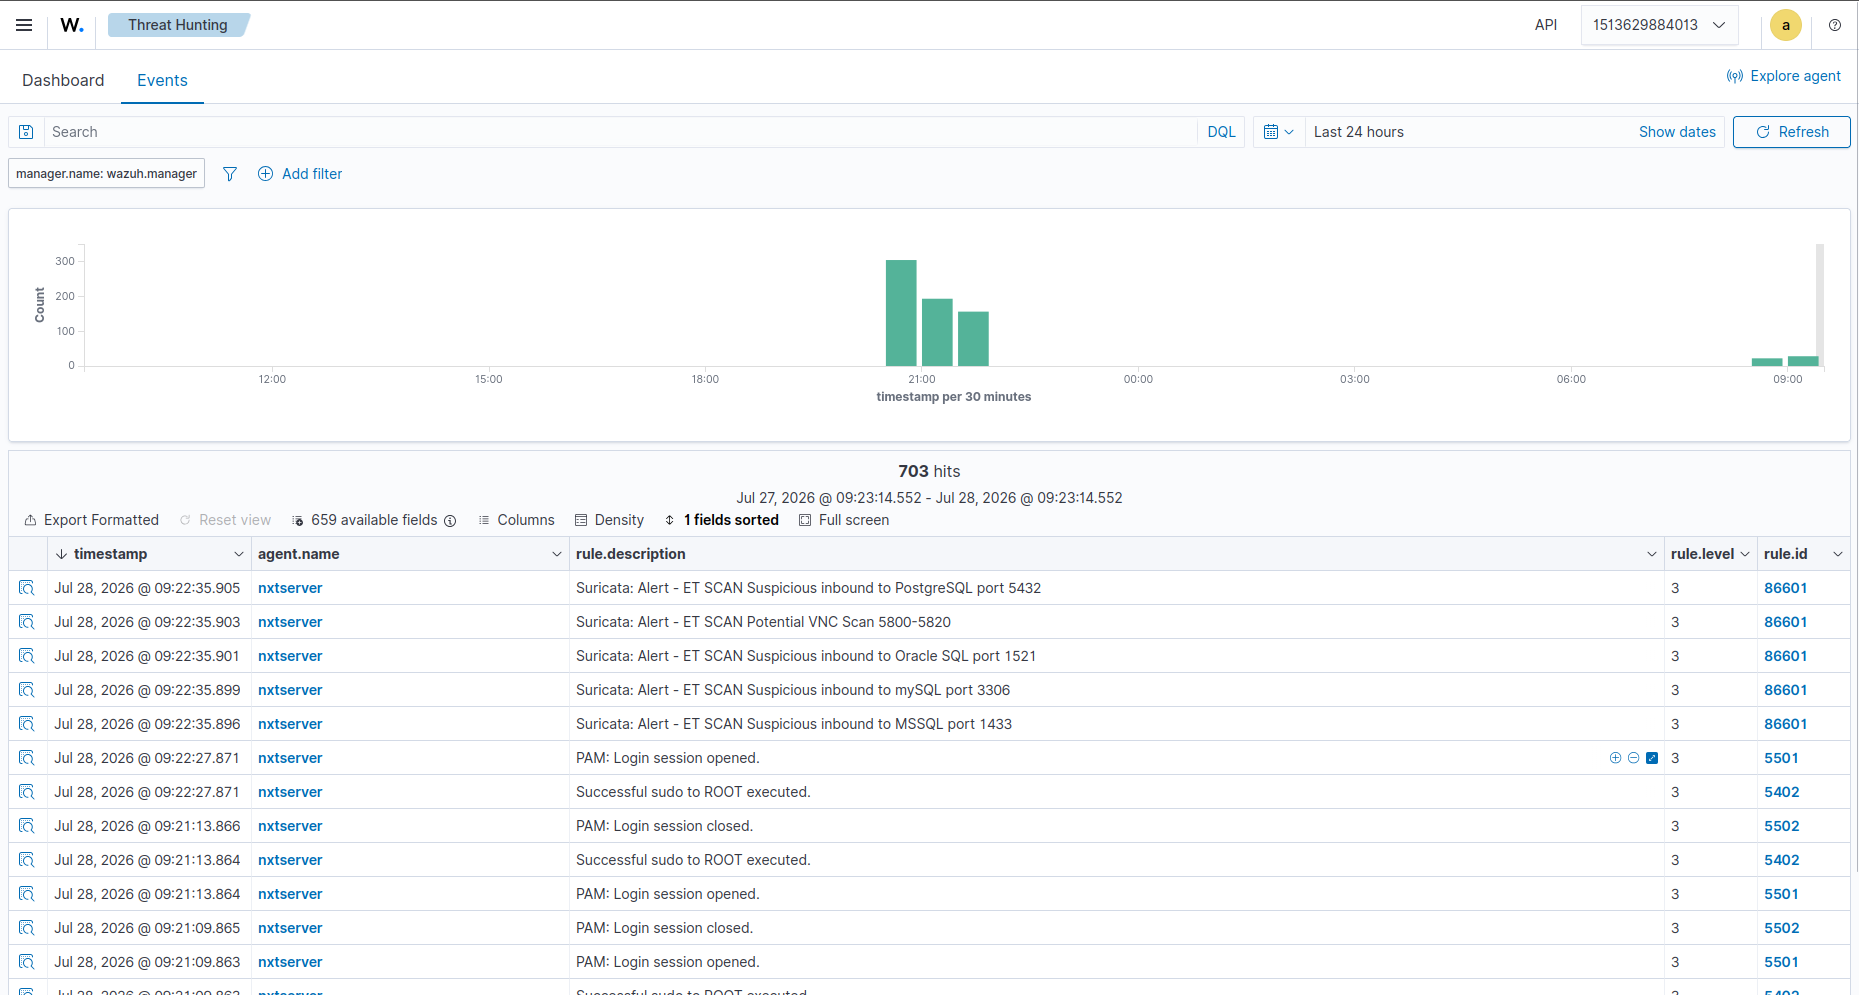
A rebuilt two-layer SOC lab, Wazuh watching the host and Suricata watching the wire, built around one question: what does network monitoring catch that host monitoring doesn't.
I work out what happened.
Cybersecurity student in Singapore. Give me a pile of logs and I'll tell you the story in them, including the parts I got wrong on the way.
Competed with NxT, representing ITE College West. The team solved 9 challenges across pwn, reverse engineering, cryptography, misc, and AI.
See the team result & write-upsI'm a cybersecurity student at the Institute of Technical Education in Singapore, and I learn by building. I care more about understanding a system than about being able to say I used it.
Twelve lines from an auth.log. Click the ones that worry you,
then run the rules and see what a small detection engine would have
caught, and what it would have missed.
A rebuilt two-layer SOC lab, Wazuh watching the host and Suricata watching the wire, built around one question: what does network monitoring catch that host monitoring doesn't.
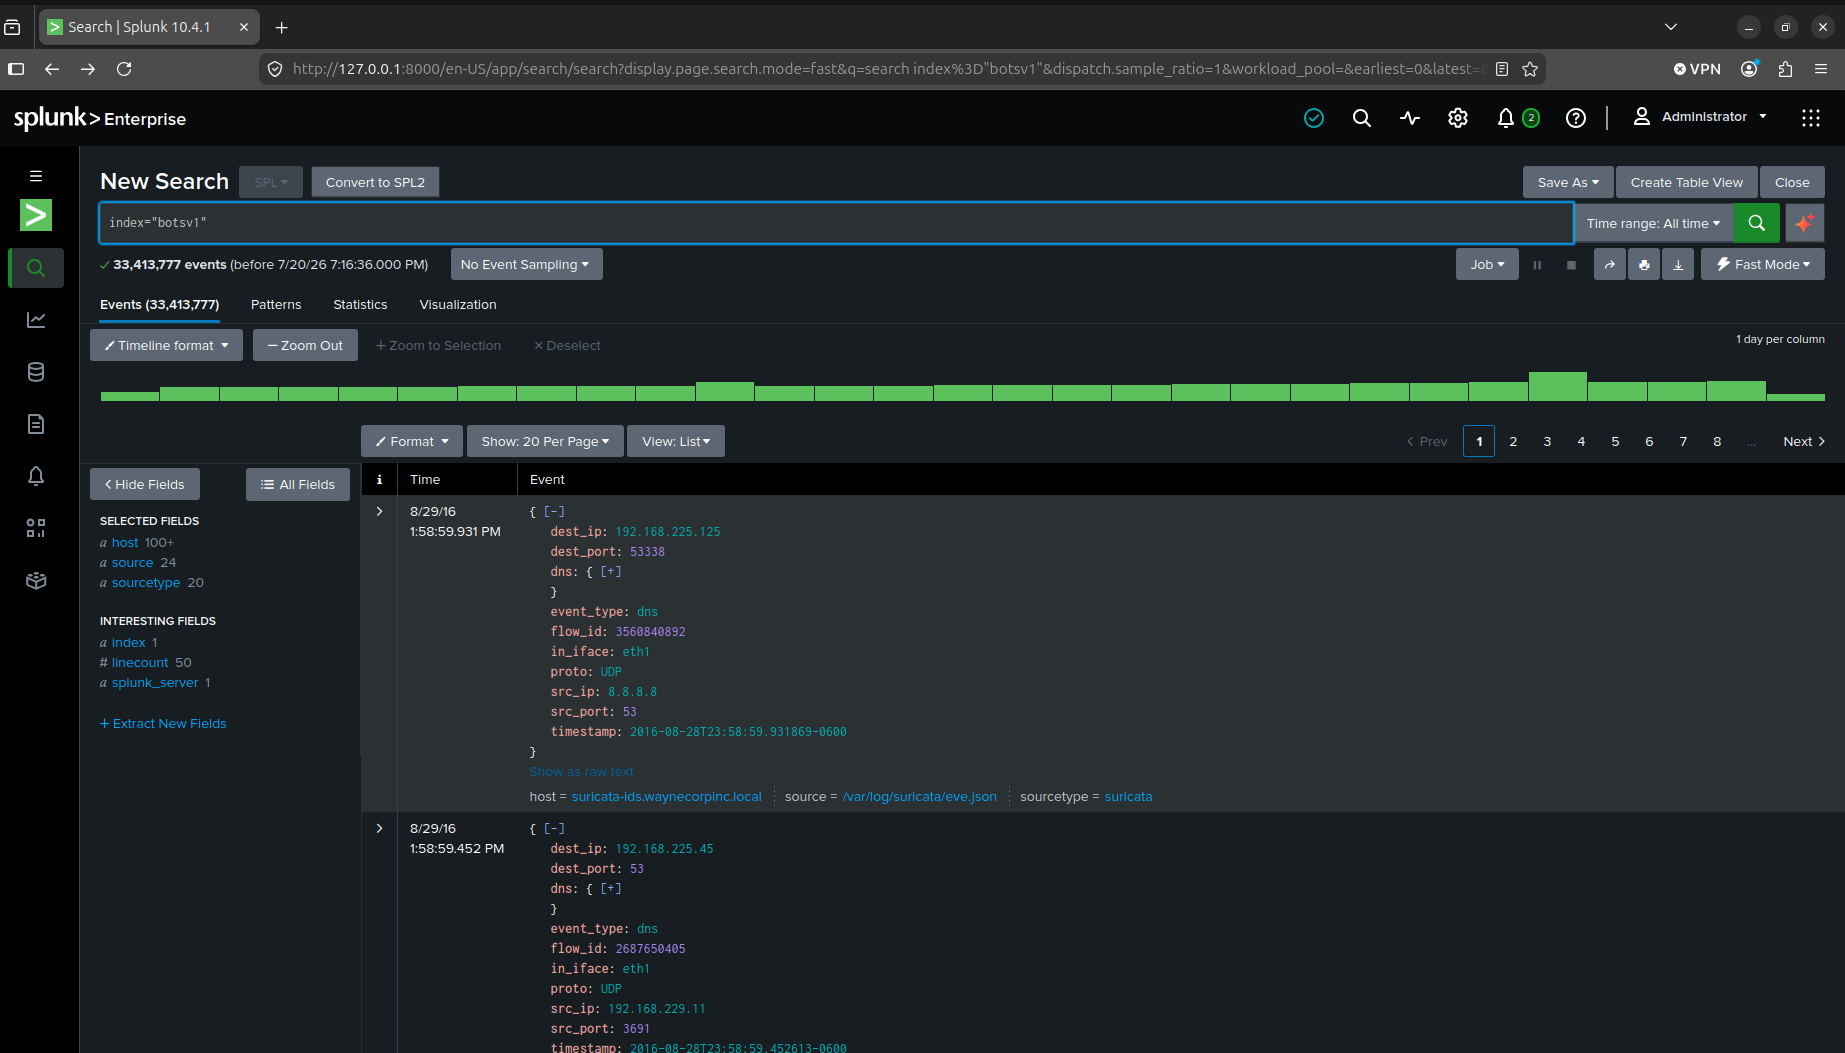
Two write-ups working through Splunk's own 33-million-event BOTSv1 training dataset as the defender, a website defacement and a ransomware outbreak on the same simulated network.
A capstone investigation from TryHackMe's SOC Level 1 path. One fake PDF on the CEO's machine, followed through Kibana to a DCSync and ransomware on the domain controller two hours later.
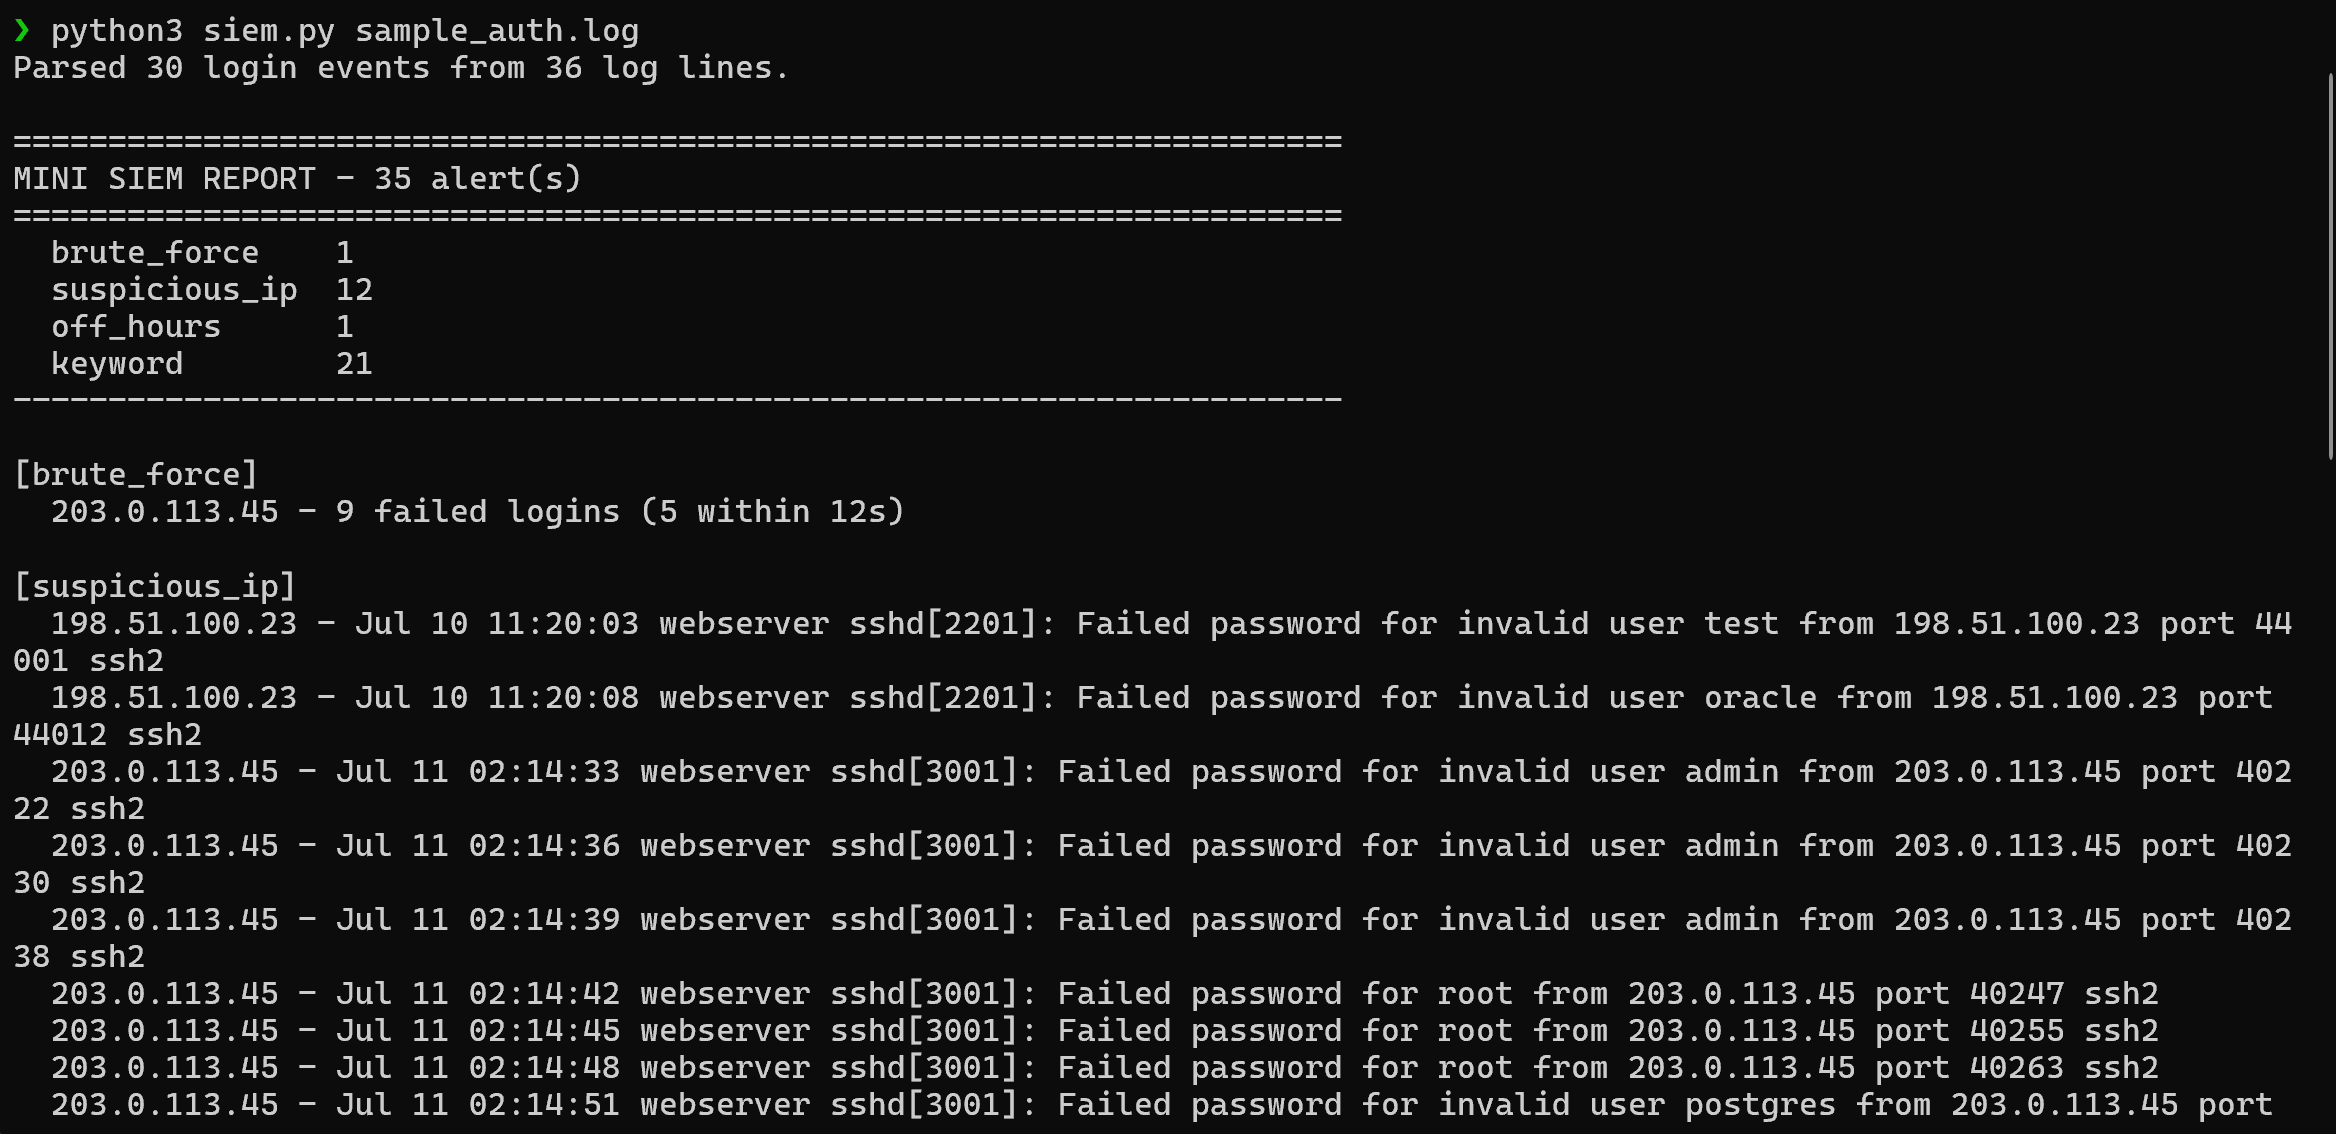
A Python tool that parses a Linux auth log once and runs four detection rules over it, then prints a ranked alert report.